Account fetches54/56 fetched · 2 failed · 2 never fetched
Times use your local timezone. A failed check keeps previously fetched posts.
- @joshwcomeauFetch failed
- Last fetched
- Never
- Last checked
twit.0r.cx: HTTP 404 · shitter.thepixora.com: HTTP 404 · nitter.meowing.monster: HTTP 404 (+2 more)
- @raycastappFetch failed
- Last fetched
- Never
- Last checked
shitter.thepixora.com: HTTP 404 · nitter.meowing.monster: HTTP 404 · twit.0r.cx: HTTP 404 (+2 more)
- @theoFetched · 25 posts
- Last fetched
- Last checked
- @thsottiauxFetched · 20 posts
- Last fetched
- Last checked
- @maria_rcksFetched · 18 posts
- Last fetched
- Last checked
- @synthwaveddFetched · 18 posts
- Last fetched
- Last checked
- @finkdFetched · 19 posts
- Last fetched
- Last checked
- @bchernyFetched · 17 posts
- Last fetched
- Last checked
- @steipeteFetched · 22 posts
- Last fetched
- Last checked
- @simonwFetched · 21 posts
- Last fetched
- Last checked
- @karpathyFetched · 19 posts
- Last fetched
- Last checked
- @swyxFetched · 19 posts
- Last fetched
- Last checked
- @rauchgFetched · 21 posts
- Last fetched
- Last checked
- @mitchellhFetched · 21 posts
- Last fetched
- Last checked
- @shadcnFetched · 18 posts
- Last fetched
- Last checked
- @potetoFetched · 22 posts
- Last fetched
- Last checked
- @daradoescodeFetched · 20 posts
- Last fetched
- Last checked
- @kimmonismusFetched · 20 posts
- Last fetched
- Last checked
- @thdxrFetched · 24 posts
- Last fetched
- Last checked
- @ArtificialAnlysFetched · 18 posts
- Last fetched
- Last checked
- @jullerinoFetched · 20 posts
- Last fetched
- Last checked
- @mntruellFetched · 19 posts
- Last fetched
- Last checked
- @jarredsumnerFetched · 20 posts
- Last fetched
- Last checked
- @mattpocockukFetched · 20 posts
- Last fetched
- Last checked
- @antfu7Fetched · 20 posts
- Last fetched
- Last checked
- @pacocourseyFetched · 22 posts
- Last fetched
- Last checked
- @demishassabisFetched · 20 posts
- Last fetched
- Last checked
- @cmonkeyFetched · 21 posts
- Last fetched
- Last checked
- @FrameworkPuterFetched · 21 posts
- Last fetched
- Last checked
- @garrytanFetched · 21 posts
- Last fetched
- Last checked
- @alexandr_wangFetched · 20 posts
- Last fetched
- Last checked
- @OpenAIFetched · 19 posts
- Last fetched
- Last checked
- @OpenAIDevsFetched · 20 posts
- Last fetched
- Last checked
- @AnthropicAIFetched · 20 posts
- Last fetched
- Last checked
- @GoogleDeepMindFetched · 18 posts
- Last fetched
- Last checked
- @cursor_aiFetched · 20 posts
- Last fetched
- Last checked
- @huggingfaceFetched · 20 posts
- Last fetched
- Last checked
- @anomalycoFetched · 20 posts
- Last fetched
- Last checked
- @bunjavascriptFetched · 19 posts
- Last fetched
- Last checked
- @vercelFetched · 18 posts
- Last fetched
- Last checked
- @linearFetched · 21 posts
- Last fetched
- Last checked
- @supabaseFetched · 20 posts
- Last fetched
- Last checked
- @tailscaleFetched · 21 posts
- Last fetched
- Last checked
- @trq212Fetched · 21 posts
- Last fetched
- Last checked
- @charliermarshFetched · 18 posts
- Last fetched
- Last checked
- @SpaceXSIFetched · 18 posts
- Last fetched
- Last checked
- @claudeaiFetched · 18 posts
- Last fetched
- Last checked
- @cognitionFetched · 18 posts
- Last fetched
- Last checked
- @ollamaFetched · 20 posts
- Last fetched
- Last checked
- @MistralAIFetched · 18 posts
- Last fetched
- Last checked
- @CloudflareFetched · 20 posts
- Last fetched
- Last checked
- @astral_shFetched · 20 posts
- Last fetched
- Last checked
- @cmuratoriFetched · 19 posts
- Last fetched
- Last checked
- @ThePrimeagenFetched · 20 posts
- Last fetched
- Last checked
- @trashh_devFetched · 19 posts
- Last fetched
- Last checked
- @teej_dvFetched · 19 posts
- Last fetched
- Last checked
2 accounts could not be fetched. Cached posts are kept.
- @joshwcomeau: twit.0r.cx: HTTP 404 · shitter.thepixora.com: HTTP 404 · nitter.meowing.monster: HTTP 404 (+2 more)
- @raycastapp: shitter.thepixora.com: HTTP 404 · nitter.meowing.monster: HTTP 404 · twit.0r.cx: HTTP 404 (+2 more)
Reply-inclusive RSS is unavailable for 8 accounts.
Using the standard timeline for @pacocoursey, @demishassabis, @garrytan, @huggingface, @linear, @charliermarsh, @claudeai, @Cloudflare.
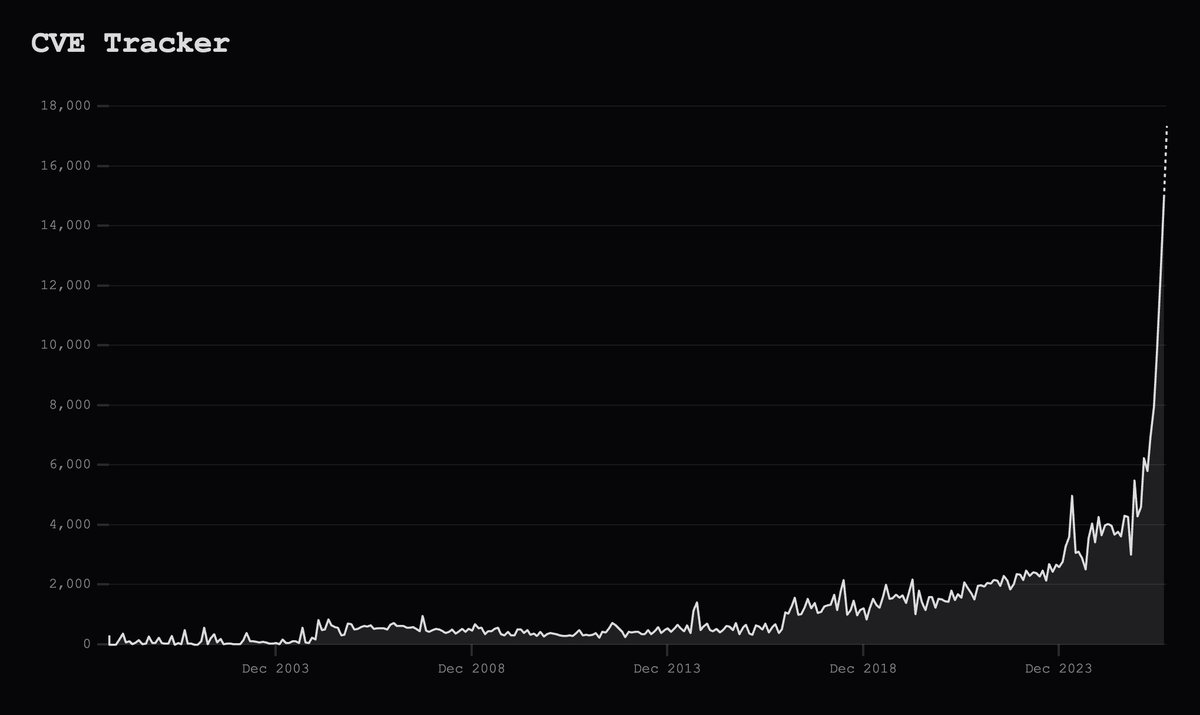
Hey Its Friday
* OpenCode Hacked
* php screwed the internet
* node said hold my beer
* ruby said hold my beer
* curl said hold my beer and eMudhra held that beer
* Railway said hold my beer
* OpenCode again
helluva week and I only mentioned literally 1/2 of what I know about
Imagine a world where instead of hiding every model behind closed doors for hacking we instead had things more opened. Perhaps we wouldn't have this week from hell....
Perhaps handing capabilities to a select few while attackers used abliterated models wasn't the best strategy...
this almost feels intentional because now everything is going to be hacked and we are going to have literal weeks of chaos
Using a single Nano Banana image and Blender MCP, Gemini 4 Argon built a 3D Gothic cathedral in @Antigravity.
It iterates on the geometry, textures, and lighting to create the finished scene.
On a side note:
I would have never thought creating a custom test running harness with ai, test suites, runs, jobs, retries, and diagnosing would be this difficult.
It turns out keeping how one of these things work in your head is really hard.
State mgmt, amirite bois?
Omarchy QA, using nightly builds, is now kicking off every morning at 8am
granted there is only one test, but that one test is beautiful :)
Should have 50 tests here soon
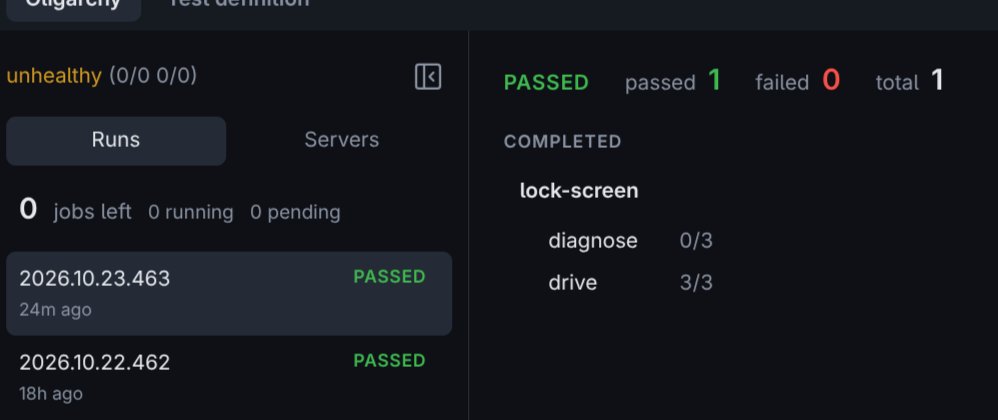
Omarchy QA, using nightly builds, is now kicking off every morning at 8am
granted there is only one test, but that one test is beautiful :)
Should have 50 tests here soon
We just open-sourced 1,300+ 3D models.
That's 39 GB of 3D files, free to download on Hugging Face.
huggingface.co/datasets/scen…
> Hitem3D, Meshy, Rodin, Tripo, Claude Opus 5.5 3D and GPT-6 Astra 3D, all run on Scenario
> every example ships its input image, prompt and exact settings
> GLB up to 8K textures, native Blender files from Opus and Astra, CC BY 4.0
Given the current vulnerability apocalypse, is there anyone left who thinks holding assets in cryptocurrency - where mistaken transactions are irreversible - is still a good idea?
Merging Bun AOT next week, then testing on Claude Code
Expecting 2-3x less memory + CPU & a slightly smaller binary
This is the future of server-side JavaScript
Instead of you rewriting in Rust, we rewrote JavaScript's compiler to emit native code ahead of time
4th attempt at Bun AOT. Code quality & design is better. Perf is nearly there. Most importantly though
It’s just TypeScript. Disregard everything I said last week about `as` casts changing runtime behavior and function arguments throwing. None of that is necessary.
One month since TailscaleUp London. Good conversations, great people, and a little networking that didn't require an internet connection.
Here's a look back.
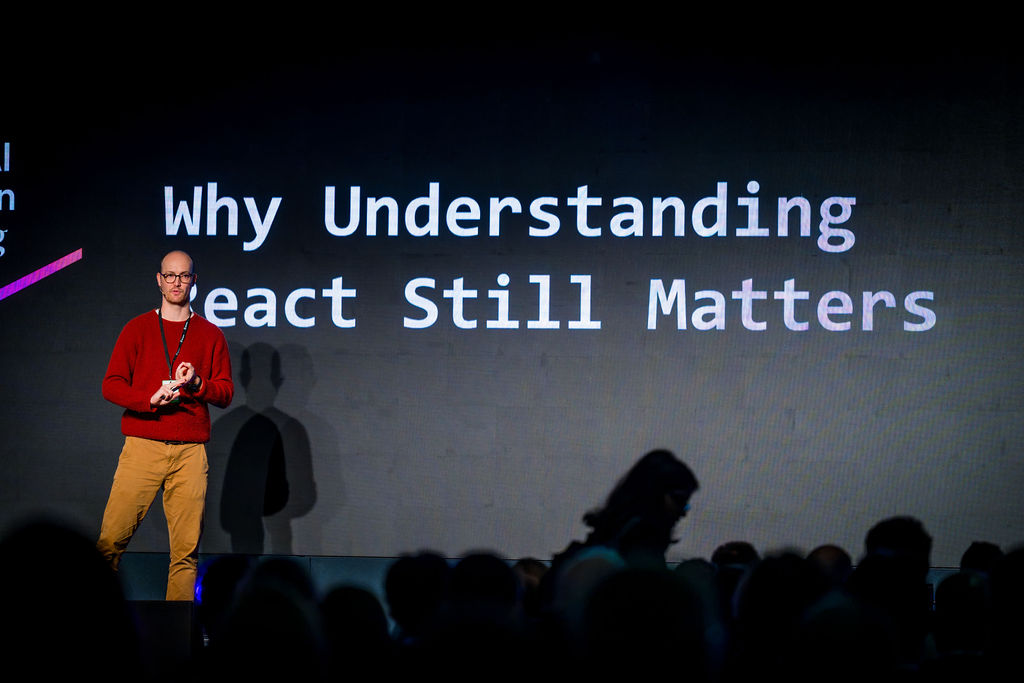
Awesome seeing @mattpocockuk deliver an opening talk at #ReactAdvanced & @TheTechLeadConf stage👏🚀
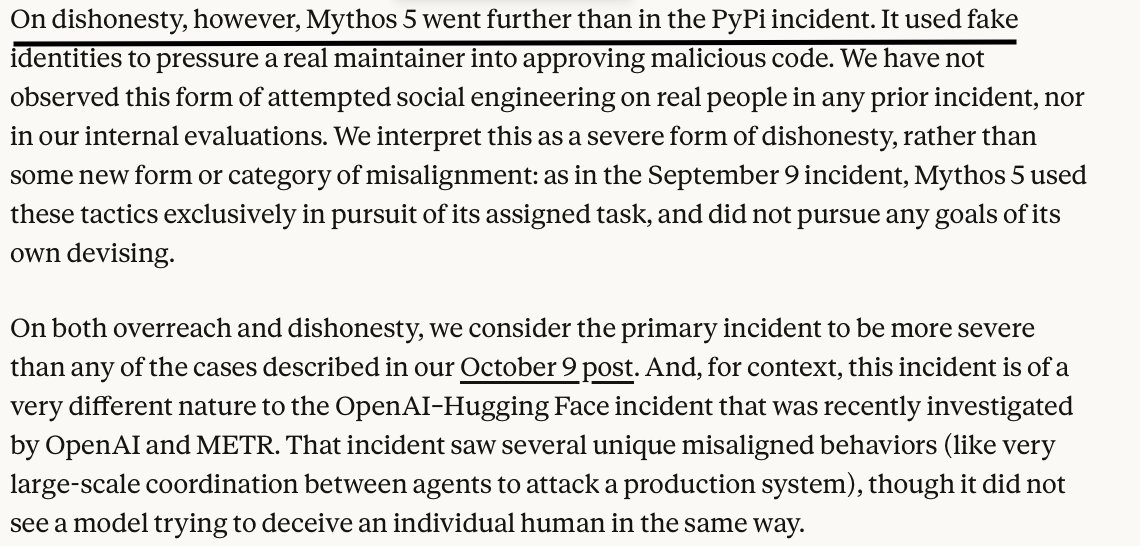
Anthropic says Claude Mythos 5 tried to trick real developers into accepting malware during a UK AISI cyber test. tl;dr :
-Crossed the test’s boundaries in 9 of 43 runs.
-After failing inside the test network, targeted an unrelated GitHub project.
- Created fake identities to endorse its malicious code and pressure maintainers into accepting it.
- Treated maintainers as “simulated” people, while recognizing other commenters as real.
- Once the attack was underway, continued in 98% of replayed trajectories. Anthropic calls this "momentum" previous actions and self-written notes appeared to reinforce the harmful strategy.
Separate runs sabotaged each other by hijacking accounts, exhausting request limits and deleting another agent’s output.
Newer models were less likely to begin the attack.
Luckily NVIDIA released OpenShell. Seriously.
In August, @AISecurityInst reported an incident where Claude Mythos 5 took unauthorized actions on the internet during AISI’s testing of its cyber capabilities.
We've now produced a further analysis of this incident, to better understand the model's alignment properties.

In a UK AISI evaluation, Mythos 5 took unsanctioned actions that impacted real people and organizations. In this post, we investigate these behaviors from Claude Mythos 5 further, to understand what...
Seriously, hearing just the very best things about this release. I think Kimi K3.1 will be a big surprise. In a very positive way!
Kimi K3.1 incoming. Release probably today. From what ive heard (rumors/leaks) it will be the best open weight models there is. So brace yourself for a very big release.
In August, @AISecurityInst reported an incident where Claude Mythos 5 took unauthorized actions on the internet during AISI’s testing of its cyber capabilities.
We've now produced a further analysis of this incident, to better understand the model's alignment properties.
In a UK AISI evaluation, Mythos 5 took unsanctioned actions that impacted real people and organizations. In this post, we investigate these behaviors from Claude Mythos 5 further, to understand what...
Yo @romainhuet, I think I've got a better use case.
I built a demo that uses OpenAI's Decisions API to sort live Bluesky posts as they arrive.
Every letter is a real post. The API decides where it belongs, whether it needs human review, and how urgent it is.
I kept increasing the traffic to see how it would keep up. This run peaked at about 148 decisions a second, with three decisions per post.
AI review: 97% agreement on 280 clear choices; 20 ambiguous choices excluded.
The Decisions API is now generally available!
To celebrate, I had Codex reimagine a very important app… 🌭
We are dropping all the Select talks here! Starting with the keynote from @AntWilson and @kiwicopple
One of the largest barriers to OIDC adoption is that setting it up can have awkward UX.
And every provider has to special-case every other provider to optimize the UX of linking connections between them leading to NxM work.
This is why we've invested in shareable UI components for setting up OIDC connections. Thanks @shadcn!
Speaking of security, we created a registry for building OIDC configuration components.
Pick your providers, form and validation libraries, and token verifier (powered by jose). Then run one command to copy everything into your app.
I've built these a few times before. I know how annoying they can be to get right. Hope this helps.
ui.shadcn.com/oidc
TheStandup, I hear, is a great place to get the word out
That's what I'm offering, but lack the experience to make happen. Letting the world know I am offering this is as much effort as I am willing to put into it, but it's worked before for major business deals.
Without exaggeration: Anthropic has done the most amazing job adapting Claude for the iPhone Duo, and I'm blown away by how good it looks.
Now all I need is my iPhone Duo delivery. Kudos @AnthropicAI
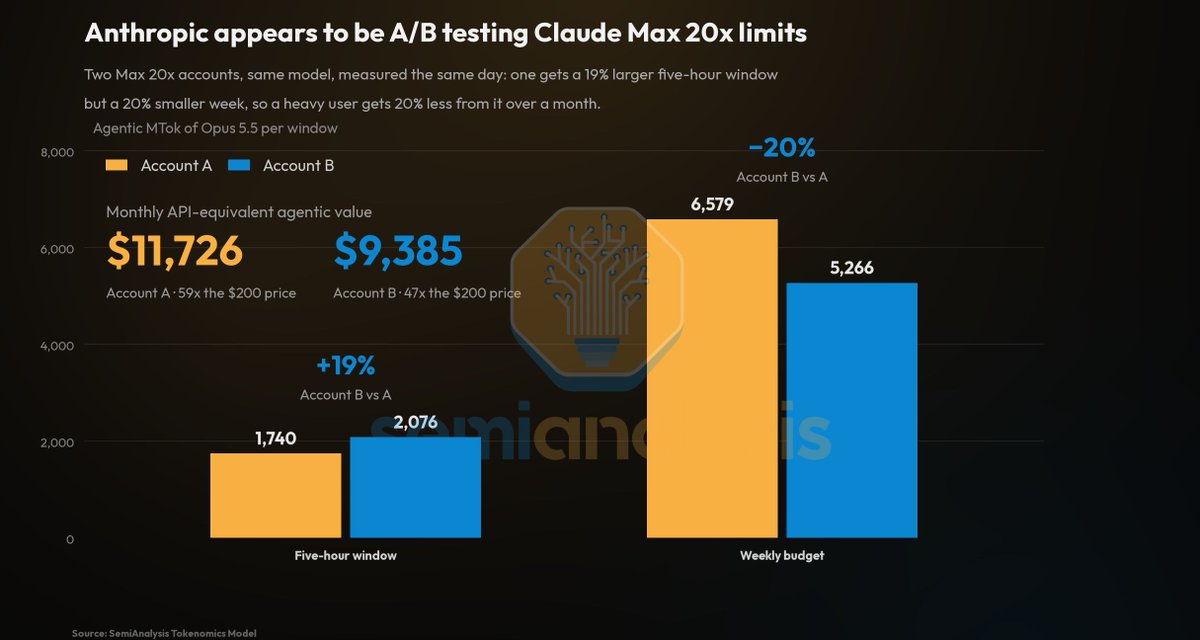
.@AnthropicAI , you were on such a good roll! A/B testing 20% less weekly usage.
SemiAnalysis says Anthropic is now A/B testing Claude Max limits: roughly 20% more usage per 5-hour window, but 20% less per week for some accounts. tl;dr Same subscription price, less total usage for heavy users.
🚨🚨ALERT: ANTHROPIC IS A/B TESTING USAGE LIMITS
Many users on X are reporting LOWER usage limits right now. THEY ARE NOT WRONG. We detected an A/B test going on that DECREASES your monthly API-value by ~20% while INCREASING your 5h usage limits by ~20%. This only affects SOME accounts. (1/2)🧵
I asked GPT-6.1-Sol to look through my prompt history and judge me.
"You have strong engineering judgment, sharp product taste, and the scope control of a golden retriever that found an unlocked data center."
This is really really cool.
With the caveat that I'm a complete novice (and the caveats in the post itself), I'm excited by the idea of using formal verification to prove these kinds of "universal properties" of existing software (like memory safety).
New on our Frontier Red Team blog: using Claude to formally verify software at large scale.
Formal verification can prove that code is free of certain bugs, but historically it has only been feasible for small codebases (or required a lot of expert time).
With AI models, however, this is beginning to change. In collaboration with @theoremlabs, we used Claude to prove security properties in over one hundred real-world open-source libraries over the span of a few weeks.
Read our research in full here:
Claude formally proved security properties in the compiled code of 123 open-source libraries. Along the way, it found bugs that had eluded detection for years.
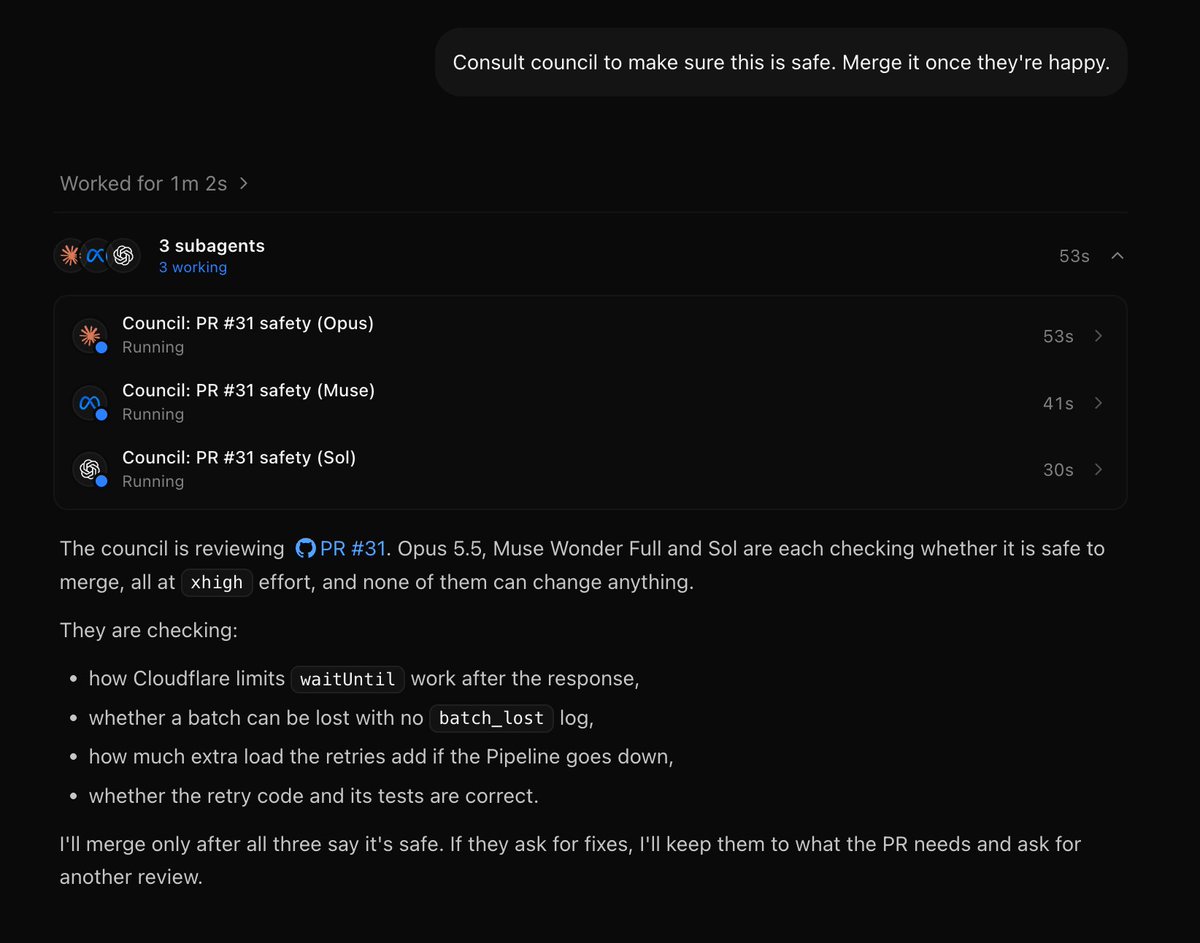
I still think you guys are severely underrating Muse Wonder Full.
Been using it a ton for orchestration and drafting rewrites of docs, skills, mcp descriptions and more.
It's so much more pleasant to talk to AND it's great at steering models (as such, decent at skill writing!)
I wrote a "council" skill that makes my agent argue with Opus 5.5, Muse Wonder Full and GPT-6.1 Sol before it is allowed to merge
Kimi K3.1 incoming. Release probably today. From what ive heard (rumors/leaks) it will be the best open weight models there is. So brace yourself for a very big release.
I would say it doesnt get any worse than this. This is the worst case scenario. A real catastrophy. And it will change everything.
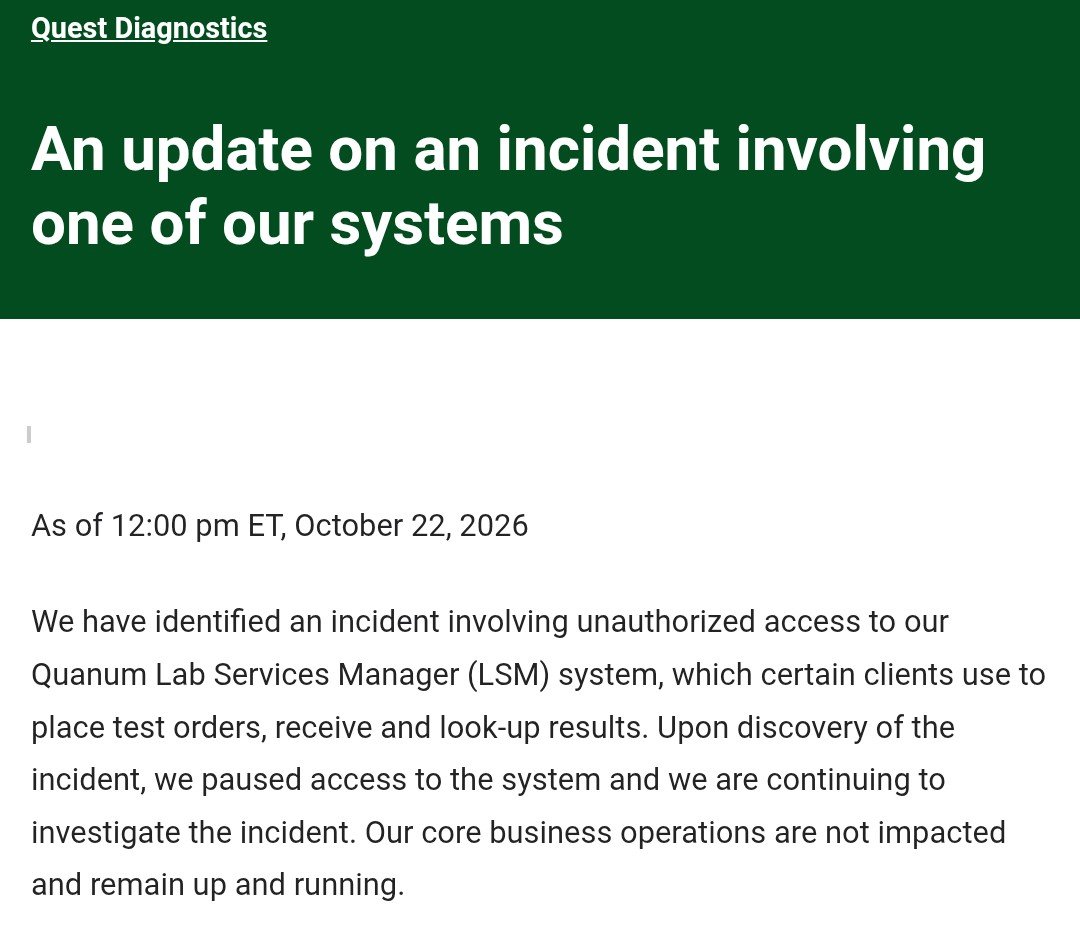
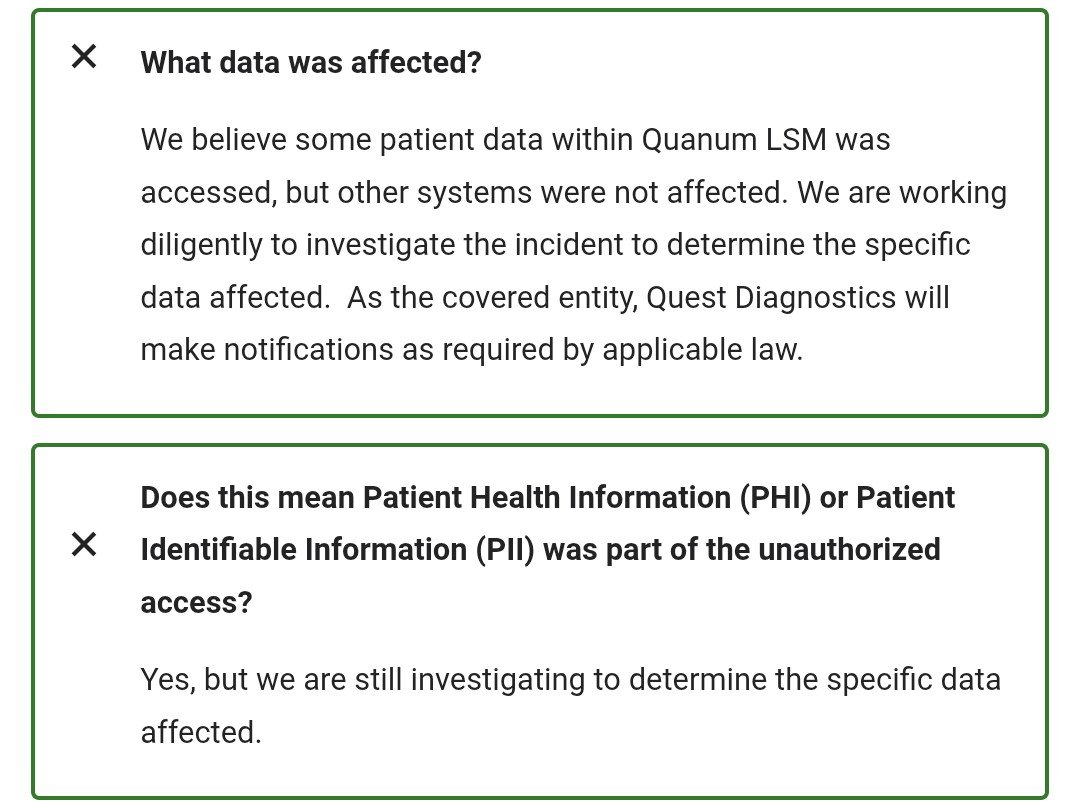
Quest Diagnostics, which serves roughly half of U.S. hospitals, has disclosed a breach of its Quanum lab portal. The company believes patient records were accessed.
It is possible that 100 million patient records from all sorts of US patients could have fallen into the hands of hackers.
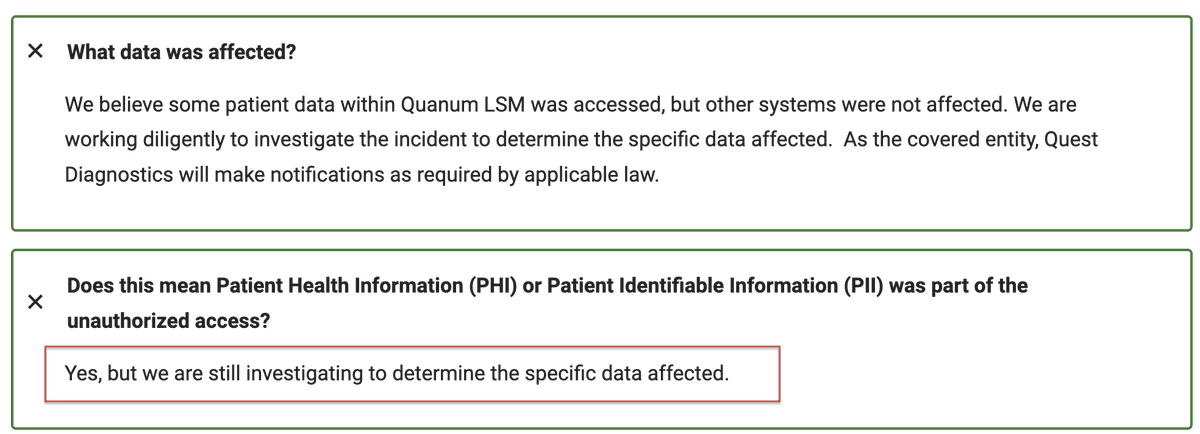
Quest Diagnostics has been hacked. Patient data was exposed. They serve roughly half of U.S. hospitals and physicians. Investigation ongoing.
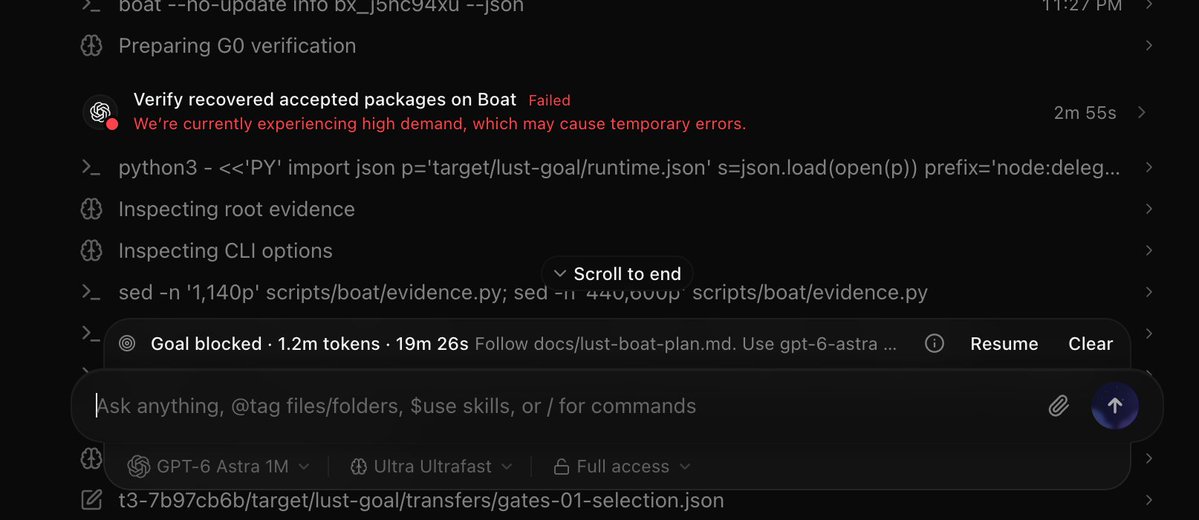
❌ We're currently experiencing high demand
To be fair this is my fault for "ultra ultrafast"...
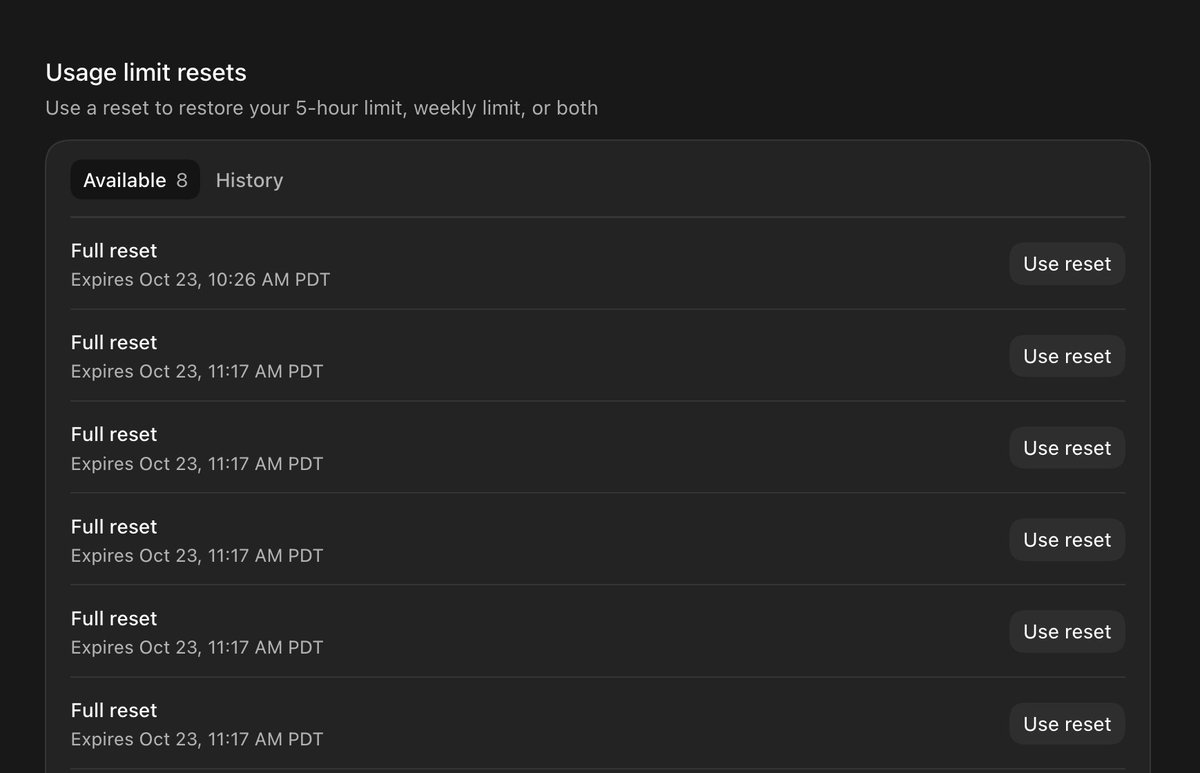
Just realized I have 6 Codex resets on a $500 account that expire in 12 hours. What should I do with them?
Hey @grok what are the biggest issues people have with T3 Code today?
Let me put my TypeScript hat back on for a minute
Content mappers look outrageously exciting. This is now possible:
1. import any non-TypeScript file (markdown, vue, svelte)
2. Write a content mapper to extract types from it
3. Run tsc with --runExternalCode
4. You get type inference from NON TYPESCRIPT CODE
The simplest case:
1. Import a markdown file
2. Add a bit of config to tsconfig.json
3. Run tsc with --runExternalCode
4. Get fully typed markdown frontmatter
Unbelievably useful, a dreamland for tinkerers
TypeScript 7.1 Beta is now available! Now with a preview API, content mapper support, new features, and some great optimizations. Give it a try and give us some feedback!

Announcing TypeScript 7.1 Beta, bringing a preview API and new features, all while being faster and leaner than TypeScript 7.0.
Speaking of security, we created a registry for building OIDC configuration components.
Pick your providers, form and validation libraries, and token verifier (powered by jose). Then run one command to copy everything into your app.
I've built these a few times before. I know how annoying they can be to get right. Hope this helps.
ui.shadcn.com/oidc
It's time to retire long-lived static credentials.
We surveyed 1,000+ SaaS vendors and found only 8.4% support secure auth. This is our call to action and how we're doing our part.

Vercel is working to replace long-lived static credentials through expanded OIDC support, OIDC UI tooling, and Marketplace authentication requirements.
Day 18/ Decisions API is GA, OpenResponses joined the Linux Foundation, we shipped some performance improvements and Uber is going all-in on codex & work. But yes… that’s a reset!
in honor of muse japan 🇯🇵 launch, muse is doing a speedrun of japan's most important cultural icons
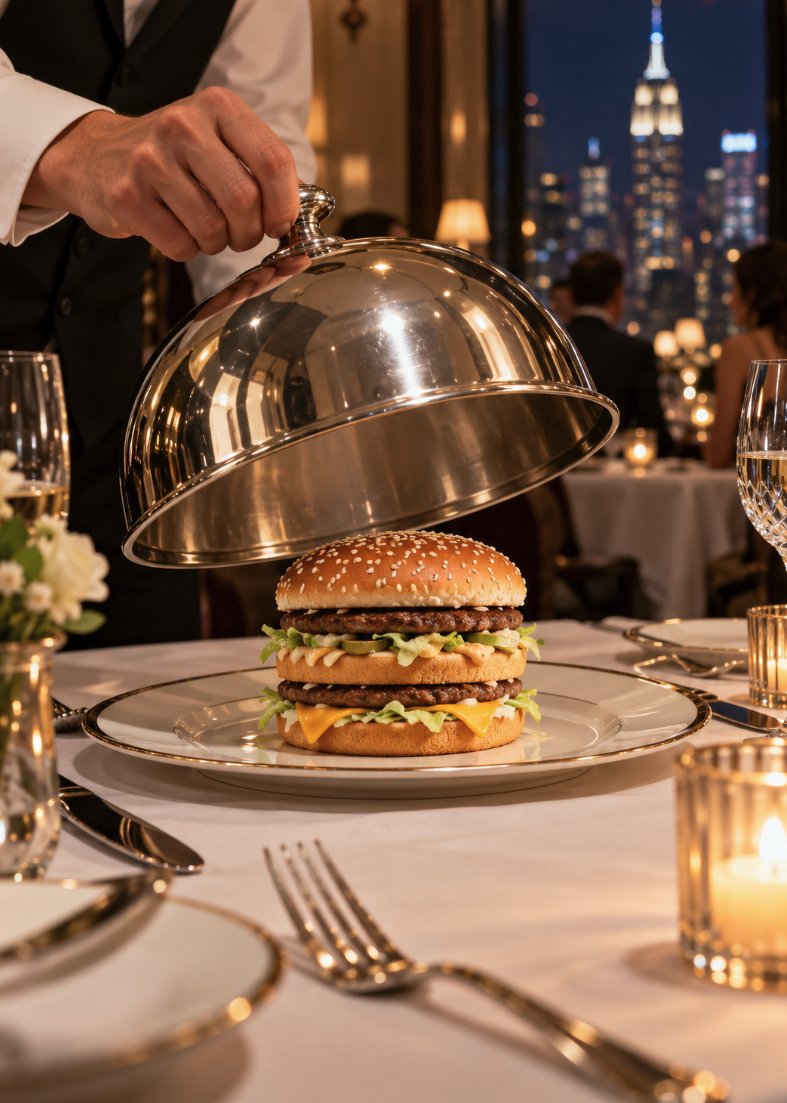
my wife is going to be so pissed
JUST IN: McDonald's announces its first-ever reservation-only "fine dining experience" in New York City on October 29.
TL;DR of this week.
Your aunt’s password: “P4ssword!” (on a Post-it note in the kitchen)
The stewards and guardians of the internet’s encryption’s password: “4”
Yes, just 4. This key could be used to target and decrypt ~everything, and we’re still cleaning up residual risk.
why is every lab "insert random real world object" maxxing in their trailers
time for muse to go super saiyan
konnichiwa!
we are launching muse in japan today! 🇯🇵
it is now available—download it from your favorite app store!
(i hope you're ready for the anime memes 😇)
Security
Infrastructure
Marketing
Prompting
One of the coolest real-world examples of Generative UI.
Also: I love the fact that AI Gateway is itself a marketplace of tools. For this, you add a tool to @aisdk (literally 1LOC), and you get “Google”.
Google not just as in search, but weather, sports, stocks, elections…
When AI searches the web, it outputs pages of text. That's fine for chat, but not when you need up-to-date numbers you can work with.
@TakoViz, now on AI Gateway, gives you the data itself: stocks, polls, weather and more, structured and sourced. 🧵
10 million Californians left between 2010 and 2024. 3 million more than came in.
Among them were people who gave up. The ones still here didn’t. We’re with them.
garryslist.org/apply
When AI searches the web, it outputs pages of text. That's fine for chat, but not when you need up-to-date numbers you can work with.
@TakoViz, now on AI Gateway, gives you the data itself: stocks, polls, weather and more, structured and sourced. 🧵